Lab 1 – Microsoft Defender XDR
SC-200: Microsoft Security Operations Analyst
Overview
Explored the Microsoft Defender XDR portal and configured preset email security policies. Applied Standard and Strict protection profiles to the tenant domain and a leadership group, then prepared the Defender XDR workspace for the remaining labs.
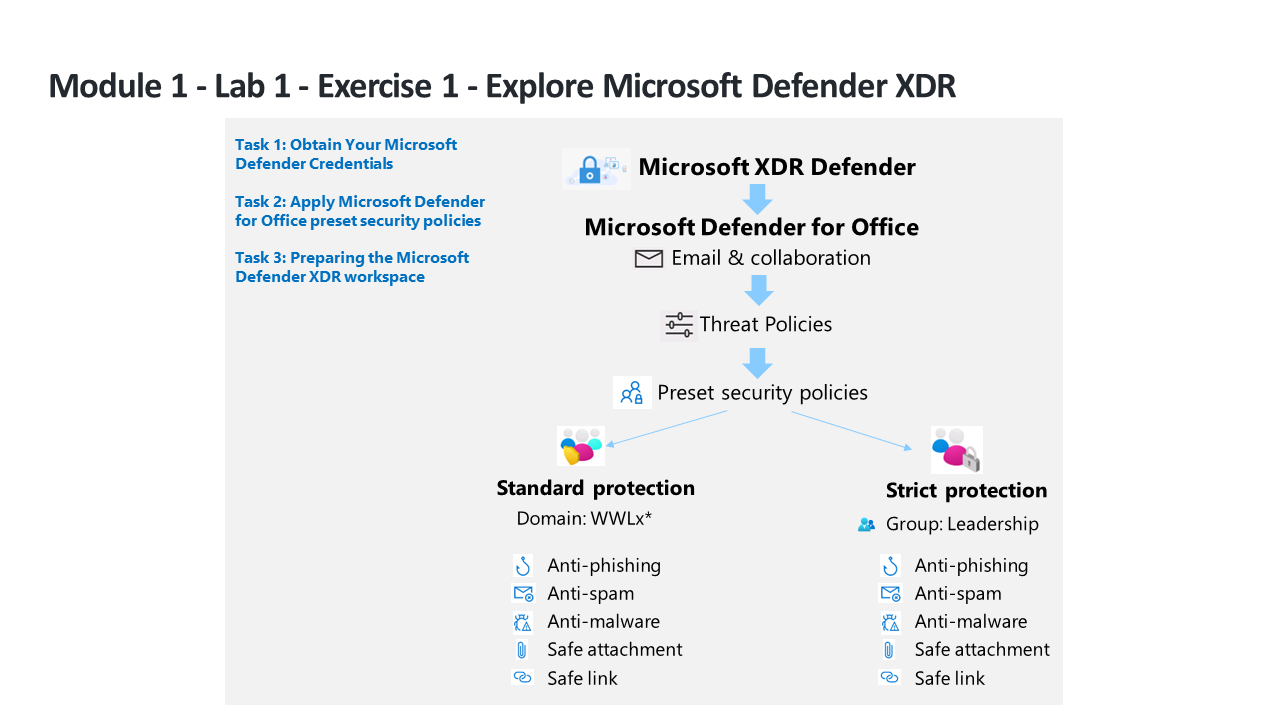
Tasks Completed
- Obtained Microsoft Defender XDR trial credentials and accessed the Defender portal
- Applied the Standard protection preset security policy to the tenant domain (anti-phishing, anti-spam, anti-malware, Safe Attachments, Safe Links)
- Applied the Strict protection preset security policy scoped to a Leadership group
- Explored the Microsoft Defender XDR portal layout: incidents, alerts, advanced hunting, and the action center
- Prepared the Defender XDR workspace for subsequent lab exercises
Environment: Microsoft 365 E5 test tenant.
Source Material
Completed using Lab 1 – Exercise 1: Explore Microsoft Defender XDR from the SC-200T00A MicrosoftLearning GitHub repository. Completed in a personal Microsoft 365 E5 test tenant.